Skip to content
  • Services
    Services
    Application Development
    • Mobile App Development
    • Blockchain Development
    By Platform
    • iOS App
    • Android App
    • React Native App
    • Flutter
    • Kotlin Multiplatform
    By Type
    • Web App Development
    • Backend and API
    • Cross-Platform Development
    • Web Development
    • Mobile Game Development
    • AR App Development
    • VR Development
    Launch & Growth
    • App Store Optimization
    • Product Launch Strategy
    • Post Launch Analytics and Iteration
    Artificial Intelligence
    AI Services
    • AI Development
    • AI App Development
    • AI Chatbot Development
    • AI Agent Development
    • Generative AI Development
    • Machine Learning Development
    • NLP Development
    • AI MVP Development
    Automation
    • AI Automation
    • System Integration & API Automation Services
    • Business Process Automation Services
    • RPA Development
    • IoT Development
    Digital Product Development
    By Engagement
    • Digital Product Development
    • Discovery Sprint
    • MVP Development
    • Product Rescue & Scaling
    • Product Strategy & Consulting
    • Custom Software Development
    • Staff Augmentation
    By Craft
    • UI/UX Design
    • Interactive Prototyping
  • Industries
    Industries
    • Healthcare App Development
    • Fitness App Development
    • Fintech App Development
    • Education App Development
    • Real Estate App Development
    • Travel App Development
    • Food Delivery App Development
    • Dating App Development
  • Locations
    Locations
    • San Francisco
    • New York
    • Austin
    • Toronto
    • London
    • Dubai
    • Singapore
  • Case Studies
  • Company
    Company
    • About
    • Blogs
    • Press & Media
    • Partnership
    • Life At Inceptives Digital
    • Leadership
    • Founder's Letter
    • Contact Us
Inceptives Digital
  • (469) 788-8527
Get In Touch
  • Blogs
App Development
  • Mobile App Security Best Practices for 2026: A Guide for Development Teams

Mobile App Security Best Practices for 2026: A Guide for Development Teams

  • Last Updated: September 28, 2026
  • Picture of Noshaba Noor Written By: Noshaba Noor
Atif Zaidy
Reviewed by: Atif Zaidy
On this page
Share
Mobile App Security Best Practices for 2026

Security rarely fails because of one critical mistake. It’s usually a series of small decisions: an exposed API, an outdated SDK, weak credential handling, data left unencrypted. 

Alone, each looks minor. Together, they are exactly what 87% of organizations reported as a mobile security incident in the past year, despite steady investment in application security.

So, when product teams invest in a mobile app development company, they need to account for these risks across architecture, APIs, third-party integrations, data storage, and release processes.

This guide maps the OWASP Mobile Top 10 risks that help teams spot them early and apply the right security measures throughout development. 

Why Mobile Apps Are Harder to Secure

Mobile applications now connect with APIs, cloud services, payment systems, analytics platforms, and third-party components. Each connection improves functionality, but it also introduces another area that requires protection. 

Security gaps in any of these layers can create costly recovery efforts, which makes choosing the right mobile app tech stack an important architectural decision. 

IBM’s 2026 Report found that the average data breach cost reached $4.44 million, highlighting why security decisions made during development can directly affect business outcomes.

A secure mobile application depends on several layers working together: 
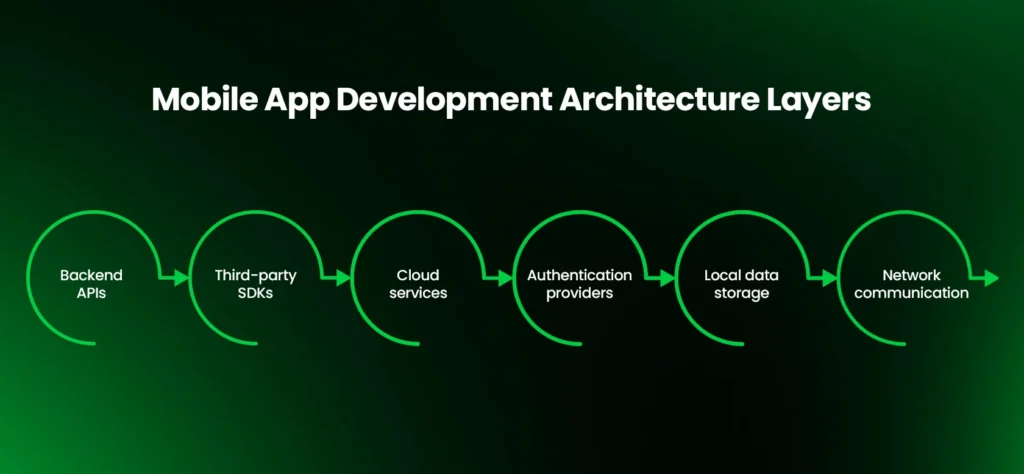
App Development Architecture Layers

Overlooking any one of these layers can create opportunities for attackers. 

OWASP Mobile Top 10 Security Risks Every App Must Address 
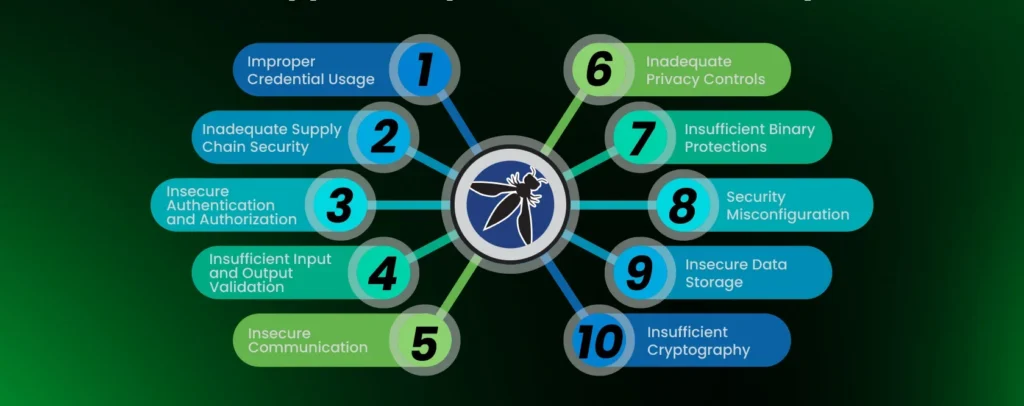
OWASP Mobile Top 10 Risks in 2026

The OWASP Mobile Top 10 outlines the security risks development teams should address when building and maintaining mobile applications. 

These risks span credential handling, authentication, data protection, insecure communication, privacy, and application integrity. 

Understanding them helps teams identify vulnerabilities early and apply the right security controls throughout the development lifecycle.

OWASP Mobile RiskPrimary ImpactAddressed In
Improper Credential UsageExposed API keys, tokens, and credentialsSecure credentials and key management
Inadequate Supply Chain SecurityVulnerable SDKs and dependenciesThird-party SDK and dependency management
Insecure Authentication and AuthorizationUnauthorized access to users or resourcesAuthentication and access control
Insufficient Input and Output ValidationMalicious requests and manipulated dataAPI security and input validation
Insecure CommunicationData interception during transmissionSecure network communication
Inadequate Privacy ControlsUnsafe handling of personal dataData privacy and protection
Insufficient Binary ProtectionsReverse engineering and code tamperingBinary protection and runtime security
Security MisconfigurationInsecure application settingsSecure development and configuration
Insecure Data StorageSensitive information exposed on the deviceData storage and encryption
Insufficient CryptographyWeak protection of sensitive dataEncryption and cryptographic key management

Here is what each category looks like in practice, based on what shows up most often in real mobile app security assessments.

1. Improper Credential Usage

API keys, access tokens, and passwords should never be treated as ordinary application data. Once exposed through source code or reverse engineering, they can provide attackers with direct access to backend systems.

2. Inadequate Supply Chain Security

Modern mobile apps rarely rely on in-house code alone. Third-party SDKs and open-source libraries speed up development, but every dependency should be verified, monitored, and updated to reduce supply chain risk.

3. Insecure Authentication and Authorization

Authenticating a user is only the first step. Applications also need to enforce what every authenticated user is allowed to access, preventing unauthorized actions across APIs and business logic.

4. Insufficient Input and Output Validation

Every request and response should be treated as untrusted until validated. Proper validation prevents malicious data from affecting application behavior or exposing backend systems to unnecessary risk.

5. Insecure Communication

Every piece of data exchanged between a mobile app and its backend should travel through a secure connection. Without proper transport security, such as HTTPS and configured TLS, attackers can intercept sensitive information, including login credentials, payment details, and personal data. 

6. Inadequate Privacy Controls

Users expect to know what information an app collects and why it needs it. Requesting unnecessary permissions or collecting more data than required increases both privacy risks and compliance concerns.

7. Insufficient Binary Protections

Once an app is installed, its code becomes a target. Without code obfuscation, integrity checks, and tamper detection, attackers can reverse engineer the application to uncover business logic, secrets, or security weaknesses.

8. Security Misconfiguration

Not every security issue comes from writing insecure code. Configuration oversights are among the common mobile app development mistakes that can create problems later. Debugging, excessive permissions, insecure cloud settings, and default configurations can even expose a well-built application.

9. Insecure Data Storage

Mobile apps often store user preferences, authentication tokens, and other sensitive information on the device. Keeping that data in unprotected storage makes it easier to access if the device or application is compromised. 

10. Insufficient Cryptography

Encryption is only as strong as its implementation. Outdated algorithms, weak key management, or improperly generated encryption keys can leave sensitive data exposed even when encryption is technically in place.

Understanding where these risks originate makes it easier to choose the right security controls later in the development process. 

Implement Mobile Security Best Practices Across the Development Lifecycle
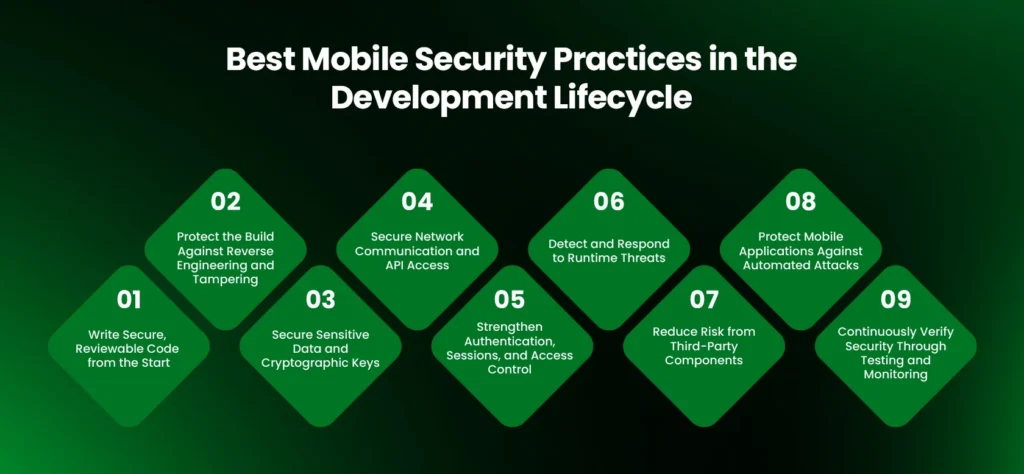
Best Mobile Security Practices in the Development Lifecycle

Every stage of the development lifecycle introduces different risks, so security controls should evolve with the product instead of being treated as a final release task.

Let’s get to know the best practices for it!

1. Write Secure, Reviewable Code from the Start

Every feature, bug fix, or integration introduces new code, and with it, new security and mobile app performance considerations. Following secure coding standards and running automated analysis throughout development helps catch vulnerabilities before they become part of the release. 

Focus areas

  • Follow secure coding guidelines.
  • Review security-critical code before every release.
  • Run SAST tools during development.
  • Include threat modeling for sensitive features.

Example: If a developer accidentally leaves an API key in the source code, a code review or automated security scan can detect it before the application is released. 

2. Protect the Build Against Reverse Engineering and Tampering

Once an app is published, anyone can download it. Code obfuscation, binary hardening, app signing, and integrity verification make it significantly harder for attackers to understand the application’s logic or modify its behavior.

These protections don’t replace secure coding, but they increase the effort required to reverse engineer the application. 

Focus areas

  • Enable code obfuscation.
  • Verify application integrity.
  • Sign every production build.
  • Disable debugging in release versions.

Example: Two shopping apps offer the same features. One uses code obfuscation, while the other doesn’t. The unobfuscated app is much easier to inspect, copy, or modify after it’s downloaded.

3. Secure Sensitive Data and Cryptographic Keys

Sensitive information deserves the same level of protection whether it’s stored on the device or transmitted to backend services. Encryption alone isn’t enough if encryption keys are exposed or stored alongside the protected data.

Use platform security features such as Android Keystore (Android Developers) and Apple Keychain Services (Apple Developer) to store cryptographic keys securely instead of embedding them in the application.

Focus areas

  • Encrypt sensitive data at rest.
  • Store keys in Android Keystore or iOS Keychain.
  • Never hardcode secrets.
  • Rotate keys when necessary.

Example: A banking app stores a user’s authentication token in Android Keystore instead of local storage, making it far more difficult to extract even if the device is compromised. 

4. Secure Network Communication and API Access

Every request between the mobile app and backend services should be authenticated, validated, and encrypted. Using HTTPS with TLS, certificate pinning where appropriate, strong API authentication, and input validation reduces the risk of interception and unauthorized access.

Protecting the API is just as important as protecting the application itself because many attacks target backend endpoints rather than the mobile interface.

Focus areas

  • Enforce HTTPS and TLS.
  • Validate all API requests.
  • Implement certificate pinning where appropriate.
  • Apply rate limiting to sensitive endpoints.

Example: When a user logs in over public Wi-Fi, HTTPS and TLS encrypt the connection so usernames, passwords, and session tokens cannot be read during transmission. 

Case in Practice: Inceptives Digital implemented secure API communication in DPS Airem to protect real-time incident reports, workforce data, and GPS updates as they moved between the mobile app and cloud services. 

5. Strengthen Authentication, Sessions, and Access Control

Authentication doesn’t end after login. User sessions should be validated throughout the application’s lifecycle to reduce the risk of stolen or expired tokens being reused.

Modern applications also benefit from multi-factor authentication, biometric authentication, and standards such as OAuth 2.0 or OpenID Connect.

Focus areas

  • Support multi-factor authentication.
  • Use biometric authentication where appropriate.
  • Expire inactive sessions.
  • Validate access tokens continuously.

Example: A user signs in on their phone but later tries to access the same account from an unfamiliar device. The application requests another verification step before allowing access. 

6. Detect and Respond to Runtime Threats

Some attacks occur only after the application reaches a user’s device. Root detection, jailbreak detection, emulator detection, Runtime Application Self-Protection (RASP), and runtime integrity checks help identify suspicious environments before sensitive operations are performed.

Runtime protection complements secure development by defending against threats that cannot be identified during testing.

Focus areas

  • Detect rooted and jailbroken devices.
  • Identify emulator-based attacks.
  • Implement runtime integrity checks.
  • Monitor for application tampering.

Example: Before processing a payment, the application checks whether the device has been rooted. If the environment appears compromised, the transaction is blocked until the risk is resolved. 

7. Reduce Risk from Third-Party Components

External SDKs and open-source libraries speed up development, but they also become part of the application’s attack surface. Teams building custom mobile applications should establish a regular dependency review process to keep third-party components secure and up to date. 

Regular dependency scanning helps identify outdated components before they become security risks. 

Focus areas

  • Review SDK permissions.
  • Scan dependencies regularly.
  • Remove unused libraries.
  • Keep third-party components updated.

Example: An application uses an analytics SDK that later receives a security patch. Updating the SDK promptly closes the vulnerability before it can be exploited. 

8. Protect Mobile Applications Against Automated Attacks

Not every attack comes from a human user. Automated bots can abuse APIs, attempt credential stuffing, scrape data, or generate fraudulent transactions at scale.

Combining device attestation, rate limiting, bot detection, and fraud monitoring helps reduce automated abuse without affecting legitimate users.

Focus areas

  • Detect bot traffic.
  • Rate limit sensitive APIs.
  • Verify trusted devices.
  • Monitor unusual request patterns.

Example: An online ticketing app notices thousands of login attempts from the same source within a few minutes. Rate limiting blocks the automated requests while genuine users continue using the app. 

9. Continuously Verify Security Through Testing and Monitoring

Security isn’t complete when the application launches. Regular penetration testing, dynamic testing, continuous monitoring, and verification against the OWASP MASVS help ensure new releases don’t introduce avoidable vulnerabilities. 

A structured mobile app testing strategy also helps identify security, performance, and reliability issues before they affect users. 

Focus areas

  • Perform SAST and DAST regularly.
  • Schedule penetration testing.
  • Validate against OWASP MASVS.
  • Monitor production environments continuously.

Example: After a major feature update, a penetration test uncovers an API that exposes more user data than intended. Fixing the issue before release prevents it from reaching production. 

Platform-Specific Security Considerations for Android and iOS
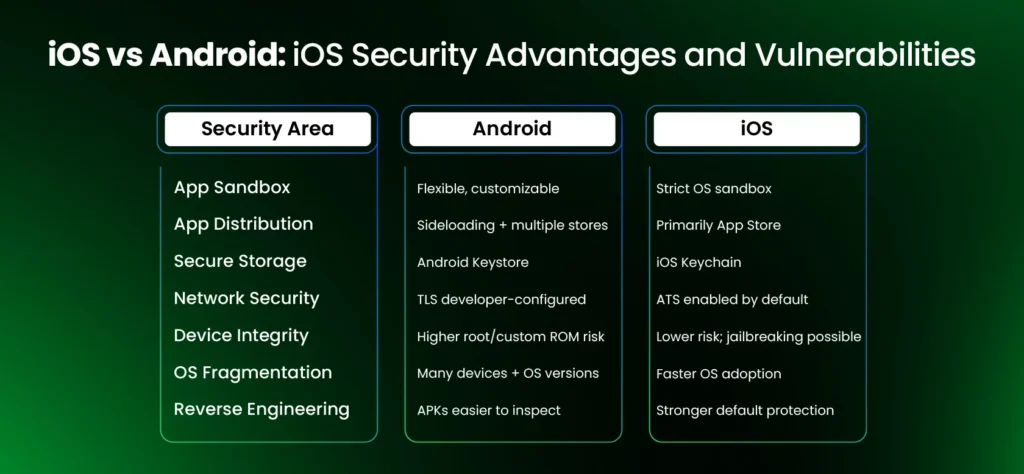
Platform-Specific Security Considerations for Android and iOS

Android and iOS follow different security models, so the same protection doesn’t always work the same way on both platforms. Understanding those differences helps development teams apply platform-specific controls instead of relying on a one-size-fits-all approach.

Security AreaAndroidiOS
Application SandboxFlexible architecture with greater customizationStrict sandbox enforced by the operating system
App DistributionSupports sideloading and multiple app storesPrimarily distributed through the App Store
Secure StorageAndroid KeystoreiOS Keychain
Network SecurityTLS must be configured by the developerApp Transport Security enabled by default
Device IntegrityHigher exposure to rooted devices and custom ROMsLower exposure, but jailbroken devices remain a risk
OS FragmentationWide range of devices and OS versionsFaster adoption of the latest iOS versions
Reverse EngineeringAPKs are generally easier to inspectIPAs provide stronger default protection

The differences above don’t make one platform universally more secure than the other. 

  • Android offers greater flexibility, but that flexibility places more responsibility on development teams building Android applications to configure security correctly. 
  • iOS starts with stronger built-in protections, although applications built for iOS still depend on secure design and implementation. 

The same principle applies to React Native, Flutter, and other cross-platform frameworks. Their security depends on the quality of the native integrations, APIs, and third-party libraries they rely on, not on the framework itself.

Wrap Up

Building a secure mobile application is all about applying the right controls throughout the development lifecycle.

The OWASP Mobile Top 10 helps identify where the biggest risks exist, while OWASP MASVS provides a practical way to verify that those risks have been addressed before release. Together, they give development teams a structured approach to building and maintaining secure mobile applications.

As applications evolve, so do the threats targeting them. Reviewing security regularly, testing new releases, and keeping dependencies up to date help reduce risk long after the first version reaches users.

Frequently Asked Questions

1. What is the OWASP Mobile Top 10, and how does it relate to mobile app security best practices?

The OWASP Mobile Top 10 identifies the most critical mobile application security risks. The best practices in this guide help reduce those risks throughout development, testing, deployment, and ongoing maintenance.

2. How much does a mobile app security audit cost, and how long does it take?

A mobile app security audit typically costs $5,000 to $30,000+ and takes one to four weeks, depending on the application’s size, complexity, supported platforms, and testing scope.

3. Is certificate pinning still necessary with modern TLS standards?

Yes. Certificate pinning provides an additional layer of protection by verifying the server’s identity, helping reduce the risk of man-in-the-middle attacks even when TLS is used correctly.

4. How often should penetration testing be performed on a mobile app handling financial or health data?

Perform mobile app penetration testing before every major release and at least annually. Applications processing financial or healthcare data often require more frequent security assessments to meet compliance requirements.

5. Does code obfuscation affect mobile app performance?

Modern code obfuscation tools such as R8 have little to no noticeable performance impact. They primarily make application code more difficult to reverse engineer without affecting the user experience.

6. Are React Native and Flutter less secure than native mobile apps?

No. React Native and Flutter can achieve the same level of security as native apps when APIs, native modules, third-party libraries, and platform security features are implemented correctly.

7. What’s the difference between OWASP MASVS and the OWASP Mobile Top 10?

The OWASP Mobile Top 10 identifies common security risks, while OWASP MASVS defines security requirements and verification criteria used to assess whether a mobile application meets those expectations.

8. Which mobile app security requirements apply under GDPR, HIPAA, or CCPA?

GDPR, HIPAA, and CCPA require organizations to protect sensitive data through secure storage, encryption, access controls, privacy safeguards, and ongoing security practices appropriate to the application’s purpose.

Picture of Noshaba Noor

Noshaba Noor

Noshaba Noor holds the role of Senior SEO Content Writer at Inceptives Digital, a mobile app development company recognized for its custom software solutions across industries. With years of hands-on experience in content strategy, her work spans website copy, blogs, and long-form guides that balance search visibility with genuine reader value. Complex technical topics become clear, accessible content, free of unnecessary jargon, in her hands. Staying updated on SEO and AEO trends, her focus is on creating content that supports organic visibility and meaningful reader engagement.
✦ Summarize with AI
ChatGPT Claude Perplexity Gemini Grok

Have a Product in Mind?

Let’s build it the right way, together
Start the Conversation
Blog / App Development / Mobile App Security Best Practices for 2026: A Guide for Development Teams

Mobile App Security Best Practices for 2026: A Guide for Development Teams

Noshaba Noor
WRITTEN BY Noshaba Noor
Atif Zaidy
REVIEWED & APPROVED BY Atif Zaidy
On This Page
Why Mobile Apps Are Harder to SecureOWASP Mobile Top 10 Security Risks Every App Must Address1. Improper Credential Usage2. Inadequate Supply Chain Security3. Insecure Authentication and Authorization4. Insufficient Input and Output Validation5. Insecure Communication6. Inadequate Privacy Controls7. Insufficient Binary Protections8. Security Misconfiguration9. Insecure Data Storage10. Insufficient CryptographyImplement Mobile Security Best Practices Across the Development Lifecycle1. Write Secure, Reviewable Code from the Start2. Protect the Build Against Reverse Engineering and Tampering3. Secure Sensitive Data and Cryptographic Keys4. Secure Network Communication and API Access5. Strengthen Authentication, Sessions, and Access Control6. Detect and Respond to Runtime Threats7. Reduce Risk from Third-Party Components8. Protect Mobile Applications Against Automated Attacks9. Continuously Verify Security Through Testing and MonitoringPlatform-Specific Security Considerations for Android and iOSWrap UpFrequently Asked Questions
Share This Article
Mobile App Security Best Practices for 2026: A Guide for Development Teams

Security rarely fails because of one critical mistake. It’s usually a series of small decisions: an exposed API, an outdated SDK, weak credential handling, data left unencrypted. 

Alone, each looks minor. Together, they are exactly what 87% of organizations reported as a mobile security incident in the past year, despite steady investment in application security.

So, when product teams invest in a mobile app development company, they need to account for these risks across architecture, APIs, third-party integrations, data storage, and release processes.

This guide maps the OWASP Mobile Top 10 risks that help teams spot them early and apply the right security measures throughout development. 

Why Mobile Apps Are Harder to Secure

Mobile applications now connect with APIs, cloud services, payment systems, analytics platforms, and third-party components. Each connection improves functionality, but it also introduces another area that requires protection. 

Security gaps in any of these layers can create costly recovery efforts, which makes choosing the right mobile app tech stack an important architectural decision. 

IBM’s 2026 Report found that the average data breach cost reached $4.44 million, highlighting why security decisions made during development can directly affect business outcomes.

A secure mobile application depends on several layers working together: 

App Development Architecture Layers

Overlooking any one of these layers can create opportunities for attackers. 

OWASP Mobile Top 10 Security Risks Every App Must Address 

OWASP Mobile Top 10 Risks in 2026

The OWASP Mobile Top 10 outlines the security risks development teams should address when building and maintaining mobile applications. 

These risks span credential handling, authentication, data protection, insecure communication, privacy, and application integrity. 

Understanding them helps teams identify vulnerabilities early and apply the right security controls throughout the development lifecycle.

OWASP Mobile RiskPrimary ImpactAddressed In
Improper Credential UsageExposed API keys, tokens, and credentialsSecure credentials and key management
Inadequate Supply Chain SecurityVulnerable SDKs and dependenciesThird-party SDK and dependency management
Insecure Authentication and AuthorizationUnauthorized access to users or resourcesAuthentication and access control
Insufficient Input and Output ValidationMalicious requests and manipulated dataAPI security and input validation
Insecure CommunicationData interception during transmissionSecure network communication
Inadequate Privacy ControlsUnsafe handling of personal dataData privacy and protection
Insufficient Binary ProtectionsReverse engineering and code tamperingBinary protection and runtime security
Security MisconfigurationInsecure application settingsSecure development and configuration
Insecure Data StorageSensitive information exposed on the deviceData storage and encryption
Insufficient CryptographyWeak protection of sensitive dataEncryption and cryptographic key management

Here is what each category looks like in practice, based on what shows up most often in real mobile app security assessments.

1. Improper Credential Usage

API keys, access tokens, and passwords should never be treated as ordinary application data. Once exposed through source code or reverse engineering, they can provide attackers with direct access to backend systems.

2. Inadequate Supply Chain Security

Modern mobile apps rarely rely on in-house code alone. Third-party SDKs and open-source libraries speed up development, but every dependency should be verified, monitored, and updated to reduce supply chain risk.

3. Insecure Authentication and Authorization

Authenticating a user is only the first step. Applications also need to enforce what every authenticated user is allowed to access, preventing unauthorized actions across APIs and business logic.

4. Insufficient Input and Output Validation

Every request and response should be treated as untrusted until validated. Proper validation prevents malicious data from affecting application behavior or exposing backend systems to unnecessary risk.

5. Insecure Communication

Every piece of data exchanged between a mobile app and its backend should travel through a secure connection. Without proper transport security, such as HTTPS and configured TLS, attackers can intercept sensitive information, including login credentials, payment details, and personal data. 

6. Inadequate Privacy Controls

Users expect to know what information an app collects and why it needs it. Requesting unnecessary permissions or collecting more data than required increases both privacy risks and compliance concerns.

7. Insufficient Binary Protections

Once an app is installed, its code becomes a target. Without code obfuscation, integrity checks, and tamper detection, attackers can reverse engineer the application to uncover business logic, secrets, or security weaknesses.

8. Security Misconfiguration

Not every security issue comes from writing insecure code. Configuration oversights are among the common mobile app development mistakes that can create problems later. Debugging, excessive permissions, insecure cloud settings, and default configurations can even expose a well-built application.

9. Insecure Data Storage

Mobile apps often store user preferences, authentication tokens, and other sensitive information on the device. Keeping that data in unprotected storage makes it easier to access if the device or application is compromised. 

10. Insufficient Cryptography

Encryption is only as strong as its implementation. Outdated algorithms, weak key management, or improperly generated encryption keys can leave sensitive data exposed even when encryption is technically in place.

Understanding where these risks originate makes it easier to choose the right security controls later in the development process. 

Implement Mobile Security Best Practices Across the Development Lifecycle

Best Mobile Security Practices in the Development Lifecycle

Every stage of the development lifecycle introduces different risks, so security controls should evolve with the product instead of being treated as a final release task.

Let’s get to know the best practices for it!

1. Write Secure, Reviewable Code from the Start

Every feature, bug fix, or integration introduces new code, and with it, new security and mobile app performance considerations. Following secure coding standards and running automated analysis throughout development helps catch vulnerabilities before they become part of the release. 

Focus areas

  • Follow secure coding guidelines.
  • Review security-critical code before every release.
  • Run SAST tools during development.
  • Include threat modeling for sensitive features.

Example: If a developer accidentally leaves an API key in the source code, a code review or automated security scan can detect it before the application is released. 

2. Protect the Build Against Reverse Engineering and Tampering

Once an app is published, anyone can download it. Code obfuscation, binary hardening, app signing, and integrity verification make it significantly harder for attackers to understand the application’s logic or modify its behavior.

These protections don’t replace secure coding, but they increase the effort required to reverse engineer the application. 

Focus areas

  • Enable code obfuscation.
  • Verify application integrity.
  • Sign every production build.
  • Disable debugging in release versions.

Example: Two shopping apps offer the same features. One uses code obfuscation, while the other doesn’t. The unobfuscated app is much easier to inspect, copy, or modify after it’s downloaded.

3. Secure Sensitive Data and Cryptographic Keys

Sensitive information deserves the same level of protection whether it’s stored on the device or transmitted to backend services. Encryption alone isn’t enough if encryption keys are exposed or stored alongside the protected data.

Use platform security features such as Android Keystore (Android Developers) and Apple Keychain Services (Apple Developer) to store cryptographic keys securely instead of embedding them in the application.

Focus areas

  • Encrypt sensitive data at rest.
  • Store keys in Android Keystore or iOS Keychain.
  • Never hardcode secrets.
  • Rotate keys when necessary.

Example: A banking app stores a user’s authentication token in Android Keystore instead of local storage, making it far more difficult to extract even if the device is compromised. 

4. Secure Network Communication and API Access

Every request between the mobile app and backend services should be authenticated, validated, and encrypted. Using HTTPS with TLS, certificate pinning where appropriate, strong API authentication, and input validation reduces the risk of interception and unauthorized access.

Protecting the API is just as important as protecting the application itself because many attacks target backend endpoints rather than the mobile interface.

Focus areas

  • Enforce HTTPS and TLS.
  • Validate all API requests.
  • Implement certificate pinning where appropriate.
  • Apply rate limiting to sensitive endpoints.

Example: When a user logs in over public Wi-Fi, HTTPS and TLS encrypt the connection so usernames, passwords, and session tokens cannot be read during transmission. 

Case in Practice: Inceptives Digital implemented secure API communication in DPS Airem to protect real-time incident reports, workforce data, and GPS updates as they moved between the mobile app and cloud services. 

5. Strengthen Authentication, Sessions, and Access Control

Authentication doesn’t end after login. User sessions should be validated throughout the application’s lifecycle to reduce the risk of stolen or expired tokens being reused.

Modern applications also benefit from multi-factor authentication, biometric authentication, and standards such as OAuth 2.0 or OpenID Connect.

Focus areas

  • Support multi-factor authentication.
  • Use biometric authentication where appropriate.
  • Expire inactive sessions.
  • Validate access tokens continuously.

Example: A user signs in on their phone but later tries to access the same account from an unfamiliar device. The application requests another verification step before allowing access. 

6. Detect and Respond to Runtime Threats

Some attacks occur only after the application reaches a user’s device. Root detection, jailbreak detection, emulator detection, Runtime Application Self-Protection (RASP), and runtime integrity checks help identify suspicious environments before sensitive operations are performed.

Runtime protection complements secure development by defending against threats that cannot be identified during testing.

Focus areas

  • Detect rooted and jailbroken devices.
  • Identify emulator-based attacks.
  • Implement runtime integrity checks.
  • Monitor for application tampering.

Example: Before processing a payment, the application checks whether the device has been rooted. If the environment appears compromised, the transaction is blocked until the risk is resolved. 

7. Reduce Risk from Third-Party Components

External SDKs and open-source libraries speed up development, but they also become part of the application’s attack surface. Teams building custom mobile applications should establish a regular dependency review process to keep third-party components secure and up to date. 

Regular dependency scanning helps identify outdated components before they become security risks. 

Focus areas

  • Review SDK permissions.
  • Scan dependencies regularly.
  • Remove unused libraries.
  • Keep third-party components updated.

Example: An application uses an analytics SDK that later receives a security patch. Updating the SDK promptly closes the vulnerability before it can be exploited. 

8. Protect Mobile Applications Against Automated Attacks

Not every attack comes from a human user. Automated bots can abuse APIs, attempt credential stuffing, scrape data, or generate fraudulent transactions at scale.

Combining device attestation, rate limiting, bot detection, and fraud monitoring helps reduce automated abuse without affecting legitimate users.

Focus areas

  • Detect bot traffic.
  • Rate limit sensitive APIs.
  • Verify trusted devices.
  • Monitor unusual request patterns.

Example: An online ticketing app notices thousands of login attempts from the same source within a few minutes. Rate limiting blocks the automated requests while genuine users continue using the app. 

9. Continuously Verify Security Through Testing and Monitoring

Security isn’t complete when the application launches. Regular penetration testing, dynamic testing, continuous monitoring, and verification against the OWASP MASVS help ensure new releases don’t introduce avoidable vulnerabilities. 

A structured mobile app testing strategy also helps identify security, performance, and reliability issues before they affect users. 

Focus areas

  • Perform SAST and DAST regularly.
  • Schedule penetration testing.
  • Validate against OWASP MASVS.
  • Monitor production environments continuously.

Example: After a major feature update, a penetration test uncovers an API that exposes more user data than intended. Fixing the issue before release prevents it from reaching production. 

Platform-Specific Security Considerations for Android and iOS

Platform-Specific Security Considerations for Android and iOS

Android and iOS follow different security models, so the same protection doesn’t always work the same way on both platforms. Understanding those differences helps development teams apply platform-specific controls instead of relying on a one-size-fits-all approach.

Security AreaAndroidiOS
Application SandboxFlexible architecture with greater customizationStrict sandbox enforced by the operating system
App DistributionSupports sideloading and multiple app storesPrimarily distributed through the App Store
Secure StorageAndroid KeystoreiOS Keychain
Network SecurityTLS must be configured by the developerApp Transport Security enabled by default
Device IntegrityHigher exposure to rooted devices and custom ROMsLower exposure, but jailbroken devices remain a risk
OS FragmentationWide range of devices and OS versionsFaster adoption of the latest iOS versions
Reverse EngineeringAPKs are generally easier to inspectIPAs provide stronger default protection

The differences above don’t make one platform universally more secure than the other. 

  • Android offers greater flexibility, but that flexibility places more responsibility on development teams building Android applications to configure security correctly. 
  • iOS starts with stronger built-in protections, although applications built for iOS still depend on secure design and implementation. 

The same principle applies to React Native, Flutter, and other cross-platform frameworks. Their security depends on the quality of the native integrations, APIs, and third-party libraries they rely on, not on the framework itself.

Wrap Up

Building a secure mobile application is all about applying the right controls throughout the development lifecycle.

The OWASP Mobile Top 10 helps identify where the biggest risks exist, while OWASP MASVS provides a practical way to verify that those risks have been addressed before release. Together, they give development teams a structured approach to building and maintaining secure mobile applications.

As applications evolve, so do the threats targeting them. Reviewing security regularly, testing new releases, and keeping dependencies up to date help reduce risk long after the first version reaches users.

Frequently Asked Questions

1. What is the OWASP Mobile Top 10, and how does it relate to mobile app security best practices?

The OWASP Mobile Top 10 identifies the most critical mobile application security risks. The best practices in this guide help reduce those risks throughout development, testing, deployment, and ongoing maintenance.

2. How much does a mobile app security audit cost, and how long does it take?

A mobile app security audit typically costs $5,000 to $30,000+ and takes one to four weeks, depending on the application’s size, complexity, supported platforms, and testing scope.

3. Is certificate pinning still necessary with modern TLS standards?

Yes. Certificate pinning provides an additional layer of protection by verifying the server’s identity, helping reduce the risk of man-in-the-middle attacks even when TLS is used correctly.

4. How often should penetration testing be performed on a mobile app handling financial or health data?

Perform mobile app penetration testing before every major release and at least annually. Applications processing financial or healthcare data often require more frequent security assessments to meet compliance requirements.

5. Does code obfuscation affect mobile app performance?

Modern code obfuscation tools such as R8 have little to no noticeable performance impact. They primarily make application code more difficult to reverse engineer without affecting the user experience.

6. Are React Native and Flutter less secure than native mobile apps?

No. React Native and Flutter can achieve the same level of security as native apps when APIs, native modules, third-party libraries, and platform security features are implemented correctly.

7. What’s the difference between OWASP MASVS and the OWASP Mobile Top 10?

The OWASP Mobile Top 10 identifies common security risks, while OWASP MASVS defines security requirements and verification criteria used to assess whether a mobile application meets those expectations.

8. Which mobile app security requirements apply under GDPR, HIPAA, or CCPA?

GDPR, HIPAA, and CCPA require organizations to protect sensitive data through secure storage, encryption, access controls, privacy safeguards, and ongoing security practices appropriate to the application’s purpose.

✦ Summarize with AI

Noshaba Noor
WRITTEN BY

Noshaba Noor

Noshaba Noor holds the role of Senior SEO Content Writer at Inceptives Digital, a mobile app development company recognized for its custom software solutions across industries. With years of hands-on experience in content strategy, her work spans website copy, blogs, and long-form guides that balance search visibility with genuine reader value. Complex technical topics become clear, accessible content, free of unnecessary jargon, in her hands. Staying updated on SEO and AEO trends, her focus is on creating content that supports organic visibility and meaningful reader engagement.

Atif Zaidy
REVIEWED & APPROVED BY

Atif Zaidy

Atif Zaidy is the Chief Technology Officer (CTO) at Inceptives Digital, specializing in software engineering, digital product development, and innovative technology solutions. He focuses on building scalable digital experiences and leveraging emerging technologies to help businesses achieve their goals.

✦ Summarize with AI

Have a Product in Mind?

Discuss your idea with our product development team.

Start the Conversation →
On This Page
Why Mobile Apps Are Harder to SecureOWASP Mobile Top 10 Security Risks Every App Must Address1. Improper Credential Usage2. Inadequate Supply Chain Security3. Insecure Authentication and Authorization4. Insufficient Input and Output Validation5. Insecure Communication6. Inadequate Privacy Controls7. Insufficient Binary Protections8. Security Misconfiguration9. Insecure Data Storage10. Insufficient CryptographyImplement Mobile Security Best Practices Across the Development Lifecycle1. Write Secure, Reviewable Code from the Start2. Protect the Build Against Reverse Engineering and Tampering3. Secure Sensitive Data and Cryptographic Keys4. Secure Network Communication and API Access5. Strengthen Authentication, Sessions, and Access Control6. Detect and Respond to Runtime Threats7. Reduce Risk from Third-Party Components8. Protect Mobile Applications Against Automated Attacks9. Continuously Verify Security Through Testing and MonitoringPlatform-Specific Security Considerations for Android and iOSWrap UpFrequently Asked Questions
Locations

Get in touch!

Scalable solutions from teams worldwide!

  • Privacy Policy
  • |
  • Terms of Services
Inceptives Digital

We build apps, digital products, and AI-powered systems for businesses that cannot afford to get it wrong.

  • info@inceptivesdigital.com
  • (469) 788-8527
Linkedin Instagram Facebook
Services
  • Mobile App Development
  • AI Development
  • Digital Product Development
  • Mobile App Development
  • AI Development
  • Digital Product Development
Industries
  • Healthcare
  • Fitness
  • Dating
  • Education
  • Real Estate
  • Travel
  • Food Delivery
  • Healthcare
  • Fitness
  • Dating
  • Education
  • Real Estate
  • Travel
  • Food Delivery
Case Studies
  • WordSmith Pro
  • DPS Airem
  • State of the Art Chiropractic
  • Family Entertainment Group
  • StakBread
  • WordSmith Pro
  • DPS Airem
  • State of the Art Chiropractic
  • Family Entertainment Group
  • StakBread
Locations
  • San Francisco
  • Toronto
  • Austin
  • New York
  • Singapore
  • London
  • Dubai
  • San Francisco
  • Toronto
  • Austin
  • New York
  • Singapore
  • London
  • Dubai
Company
  • About
  • Blog
  • Press & Media
  • Partnership
  • Life At Inceptives Digital
  • Leadership
  • Founder’s Letter
  • Contact Us
  • About
  • Blog
  • Press & Media
  • Partnership
  • Life At Inceptives Digital
  • Leadership
  • Founder’s Letter
  • Contact Us
Recognized and Reviewed On

Independent reviews and industry recognition from established B2B platforms.

Clutch Review Badge
Bark Review Badge
Trustpilot Review Badge
Our Locations
United States
New York, USA

1178 Broadway, 3rd Floor New York, NY 10001 United States

United States
San Francisco, USA

490 Post St, Ste 500 San Francisco, CA 94102 United States

United States
Austin, USA

5900 Balcones Drive, Suite 100 Austin, Texas 78731 United States

United States
Allen, USA

450 Century Parkway, Suite 250 1005 Allen, TX 75013, USA

Canda
Toronto, Canada

2482 Yonge Street Toronto, ON M4P 2H5 Canada

united kingdom
London, UK

Office 1776, 60 Tottenham Court Road, Fitzrovia, London W1T 2EW

Dubai, UAE

IFZA Business Park Building A2, Dubai Silicon Oasis Dubai, UAE

Singapore
Singapore

No. 7 Temasek Boulevard #12-07, Suntec Tower One Singapore 038987

Pakistan
Karachi, Pakistan

Office No. 1, Najeeb Center 172-B Tariq Road, PECHS Karachi 74400, Pakistan

© 2026 IT Core Solutions LLC DBA Inceptives Digital. All Rights Reserved.

  • Privacy Policy
  • Terms of Use
DMCA.com Protection Status

Get Expert Direction for Your Next Digital Product

Inceptives Digital has helped businesses across regions bring their visions to life. See what their experience says about working with us. We don’t do magic. We build with expertise.

“
Inceptives Digital has been professional, responsive, and genuinely committed to understanding our vision for Evoltion Enterprise. The team communicated clearly, explained technical details patiently, and made payments hassle-free. Special thanks to Aaron Francis for his clarity and support throughout. Highly recommend them as a transparent, easy-to-work-with technology partner
Tyrrell Gibson CEO, Evoltion Enterprise
When I came to these guys, it was just me in an idea. I’ve had ideas before that. I thought were good and sat on them only to watch others take the initiative and reap the rewards because I lacked confidence. When I had the idea for my app I figured, “Not this time.
Edward Eller, GoRyde
I absolutely recommend this company. This team is absolutely Amazing!
I can't say enough good things about them. I had tried 3 other app makers before finding them. All of them fell short in the end. The Inceptive team was the literal answer of my prayers.
DC & Owner, State of the Art Chiropractic
AWARDS & RECOGNITION
Inceptives Digital award badge 1
Top Mobile App Developers 2025
Inceptives Digital award badge 3
RightFirms company badge
Inceptives Digital award badge 5
FEATURED ON MEDIA & REVIEW PLATFORMS
Associated Press
Trustpilot
Google
The New York Times
The Globe and Mail
USA Today

Let us help you build the next innovative digital product with precision and expertise. Share your idea and get a customized roadmap to your app within 24 hours.

Fully NDA-Protected
  • Privacy Policy
  • |
  • Terms of Services

Schedule a Meeting

Loading calendar...
Calendar is taking longer than expected

Please try again, or open Calendly directly to book your meeting.

Open Calendly